
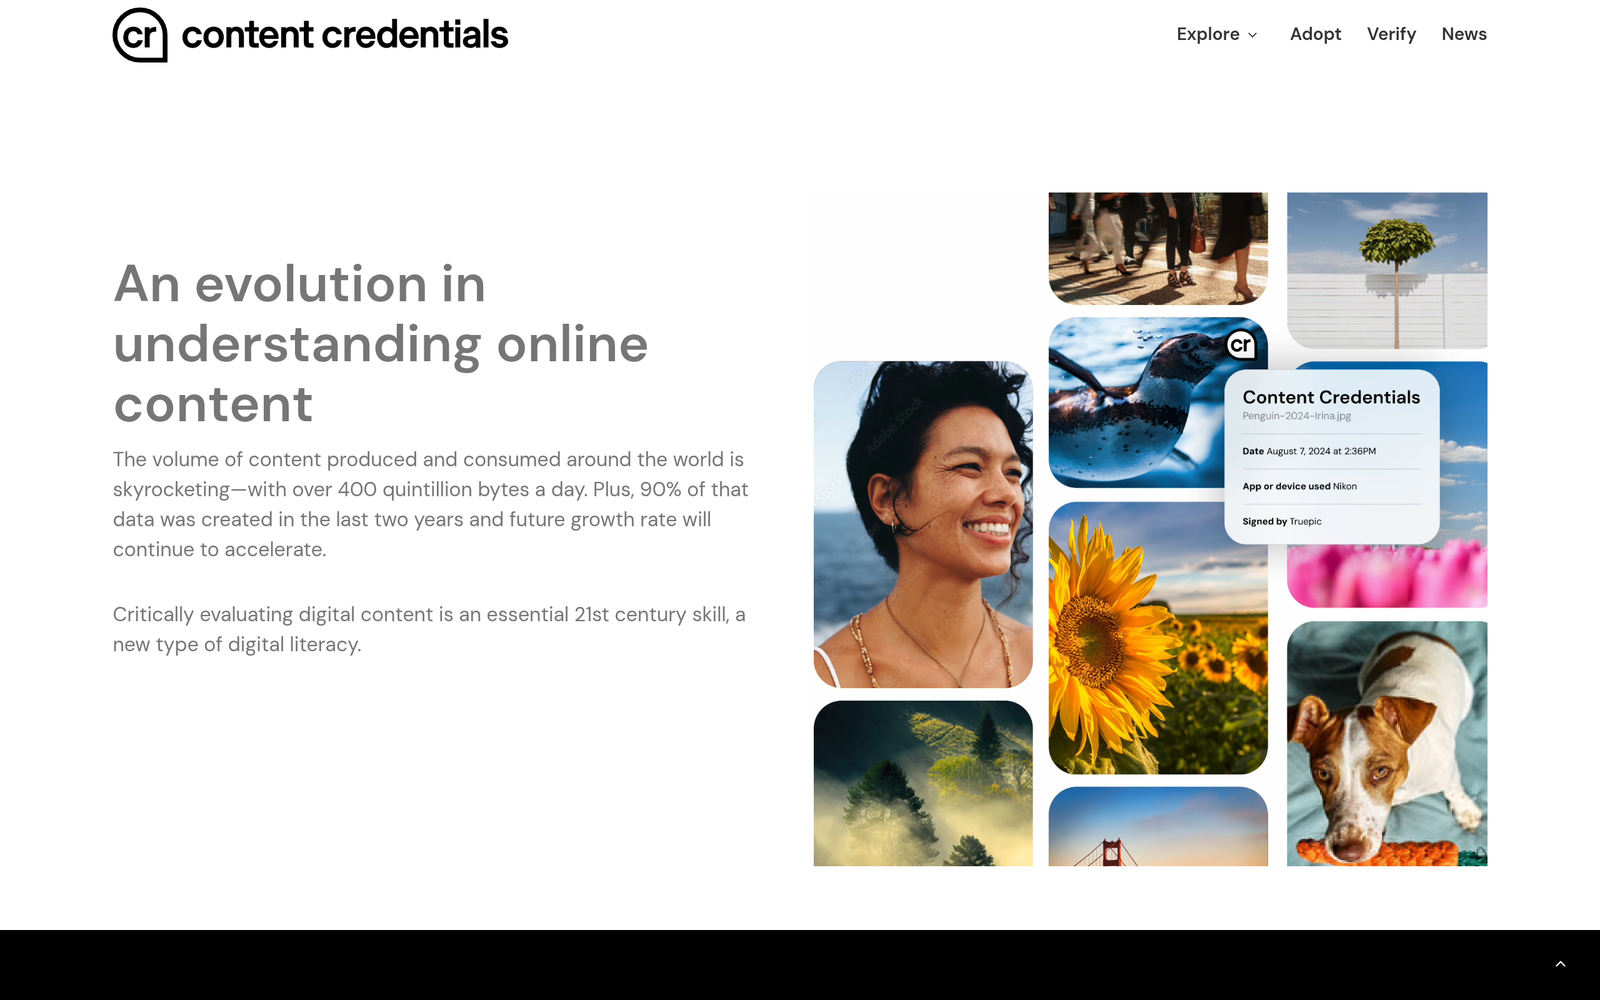
Quick Executive Summary
Digital media authenticity faces systemic challenges due to the rapid proliferation of synthetic media and accessible digital editing tools. Content Credentials addresses this by providing an open standard and digital provenance framework. Rather than acting as a traditional detection engine, it functions like a digital “nutrition label,” binding tamper-evident, cryptographically signed metadata to images, video, and documents to certify how, when, and by whom an asset was produced or modified. Hosted by the Coalition for Content Provenance and Authenticity (C2PA), it delivers a standardized, platform-agnostic layer of transparency across the content lifecycle.
What Content Credentials Is and How It Actually Works
To understand what is Content Credentials, one must distinguish between passive forensic detection and active provenance tracking. Content Credentials is an open technical specification governed by the C2PA (formed by cross-industry leaders including Adobe, Arm, Intel, Microsoft, and others). It establishes an auditable historical trail for digital files.
When an asset is captured by a supported camera, generated via an AI engine, or modified in editing software, Content Credentials cryptographically signs the file’s metadata. This signature contains details such as author identity, editing ingredients, tools used, and generation timestamps. If a file is subsequently altered without proper credentialing or if the data is tampered with, the cryptographic chain breaks, signaling that the manifest is invalid or missing.
Consumers and reviewers interact with this data through a visual “pin” or indicator on the media. Clicking this pin displays an interactive component revealing the sequence of edits, imported assets, and AI generation tags associated with that specific file.
Target Audience & Ideal Users
- News and Media Publishers: Editorial teams seeking to authenticate field assets, verify original sources, and provide audiences with verifiable proof of journalistic integrity.
- Digital Artists and Content Creators: Professionals who want tamper-evident attribution for their work and clear proof of human authorship or AI tool assistance.
- Platform Engineers and Developers: Technical teams integrating media provenance into publishing platforms, social networks, or content management systems via C2PA standards.
- Enterprise Content Teams: Organizations producing legal, medical, or regulatory visual documentation requiring an auditable creation history.
Core Features & Capabilities
The technical architecture of Content Credentials relies on several verified capabilities specified in vendor and standard documentation:
- Cryptographically Signed Manifests: Attaches tamper-evident metadata detailing software actions, parent media assets, and author information using industry-standard digital signatures.
- Visual Pin and Interactive Viewer: Provides an on-asset indicator that users can click to view a complete, human-readable chronology of how the media was assembled and edited.
- Durability via Invisible Watermarking: Designed to interface with invisible watermarking technologies to reconstruct or link back to provenance records even if metadata is stripped during transit.
- Digital Fingerprinting Integration: Supports perceptual hashing and fingerprinting systems to bind media copies back to original credentials stored in decentralized or cloud-based registries.
- C2PA Cross-Industry Compatibility: Operates strictly under open, interoperable specifications rather than a proprietary vendor format, ensuring cross-platform ingestion.
Pricing, Tier Differences, and Plan Limitations
Content Credentials is an open standard, not a commercial software-as-a-service (SaaS) tool. As a result, direct subscription fees do not apply to the core specification itself.
| Component | Cost / Model | Details & Restrictions |
|---|---|---|
| C2PA Specification & Standard | Free / Open Source | Technical specifications, developer guidelines, and architecture frameworks are publicly accessible at no charge. |
| Reference Tools & Libraries | Free / Open Source | Open-source code, SDKs, and the public verification portal are accessible for developers to build verification pipelines. |
| Third-Party Implementations | Varies by Vendor | Implementation costs depend on the supporting editing suites (e.g., Adobe Creative Cloud), camera hardware, or enterprise CMS integrations. |
Because there is no hosted centralized “Content Credentials SaaS plan,” infrastructure costs (such as signing certificates, key management services, and storage registries) must be absorbed by the deploying organization.
Key Advantages
- Tamper-Evident Architecture: Any attempt to alter the embedded manifest or edit the file outside of a compliant environment invalidates the digital signature, alerting the viewer to discrepancies.
- AI Transparency: Provides a standardized, verifiable method to disclose generative AI usage at the asset level, helping platforms comply with emerging transparency regulations.
- Vendor-Agnostic Interoperability: Because it is governed by C2PA rather than a single entity, files maintain provenance across different authoring software, hardware devices, and display engines.
- Multiple Persistence Layers: Compatibility with fingerprinting and watermarking mitigates the classic problem of metadata deletion during file transfers.
Documented Drawbacks and Limitations
- Metadata Stripping on Social Platforms: Many legacy social media networks, messaging applications, and content delivery networks (CDNs) aggressively compress or re-encode images, which strips out standard EXIF and C2PA metadata unless persistent watermarking workflows are explicitly implemented.
- Not an Automated Fake Detector: Content Credentials does not evaluate whether an untagged image is genuine or forged. An asset without credentials is simply unverified, not necessarily fraudulent.
- Implementation Complexity: Deploying Content Credentials requires compatible hardware, specialized editing software, and cryptographic infrastructure (such as X.509 certificates and secure signing servers), creating adoption friction for smaller workflows.
- Bad-Actor Circumvention: While credentials cannot be tampered with without breaking signatures, bad actors can bypass the system simply by screenshotting, scanning, or stripping the file entirely, creating an uncredentialed clone.
Who Should Consider Content Credentials vs. Who Should Look Elsewhere
Who Should Consider It
- Enterprises and publishers seeking an auditable, industry-standard mechanism to declare media provenance.
- Developers building CMS workflows, marketplaces, or media viewers that need native, standardized support for synthetic media disclosure.
- Photojournalists and photographers who work within supported hardware/software environments and need to prove original chain of custody.
Who Should Look Elsewhere
- Users seeking automated deepfake detection: Those looking for a consumer scanning app to test whether a random, unverified web file is AI-generated need AI detection tools, not provenance frameworks.
- Teams looking for Digital Rights Management (DRM): Content Credentials does not restrict copying, viewing, downloading, or unauthorized distribution; it only documents origin and editing history.
- Organizations unwilling to manage cryptographic infrastructure: Implementing Content Credentials at scale requires public key infrastructure (PKI) management and pipeline development.
Transparent Editorial Evaluation & Methodology
This assessment is a research-based technical analysis grounded in vendor documentation, C2PA technical specifications, and official organizational disclosures from contentcredentials.org. No active hardware or enterprise signing pipeline trial was conducted for this evaluation. Technical features, architecture compatibility, and pricing frameworks reflect public specifications available as of late 2024 to early 2026. Evaluation criteria prioritized cryptographic viability, open standard governance, adoption hurdles, and practical real-world persistence limitations.
Review Methodology & Source Verification
This is a research-based product analysis based on vendor documentation, publicly documented pricing, and verified technical specifications. No hands-on trial was conducted.
Last Verified: October 16, 2026
Primary Sources: Content credentials Official Documentation
Similar AI Tools You Might Like

GPTZero is an online tool that enables users to determine whether a text was written by...
"If This Image is Safe for Work" is an AI tool that analyzes images to determine...
GPTKit is a tool that helps you detect and classify text as either human-written or machine-generated...